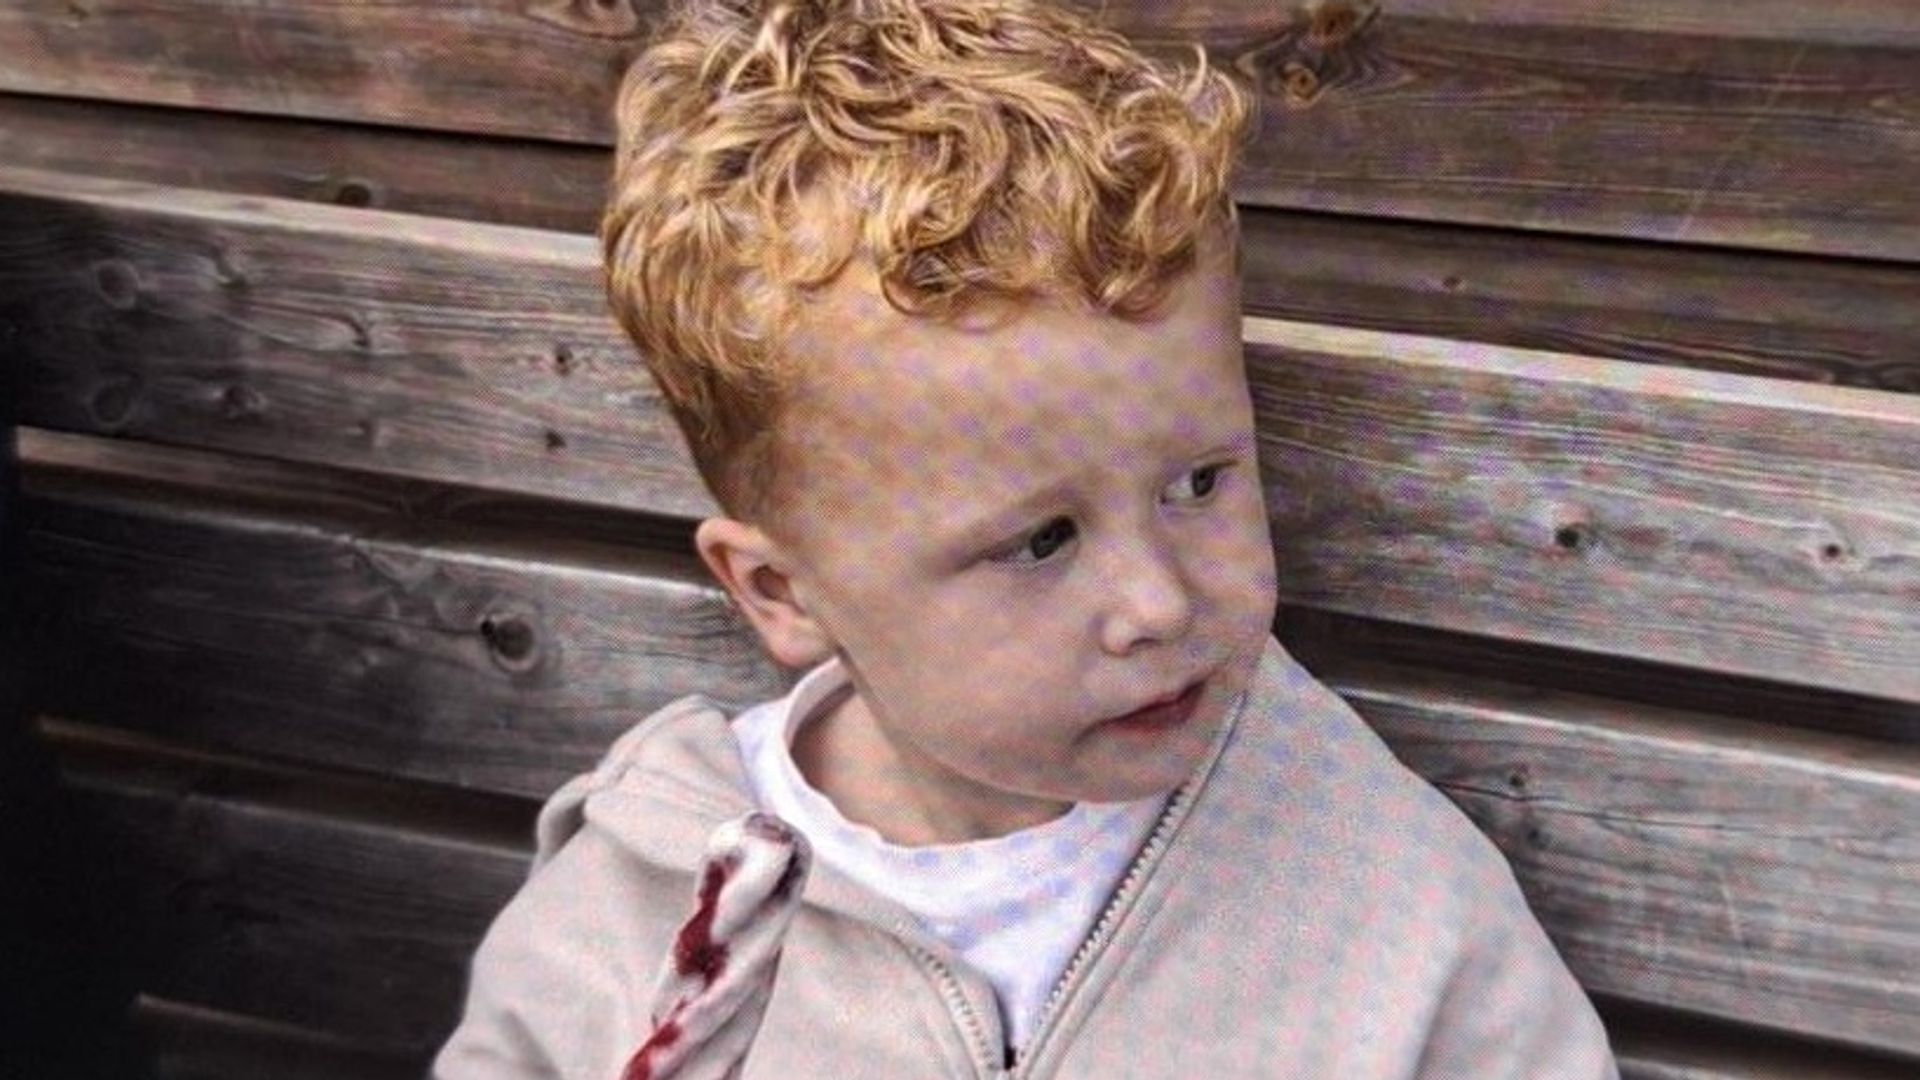
Medical data snooping inside hospitals is out of control. When the East Suffolk and North Essex NHS Foundation Trust recently had to issue an unreserved apology to the family of late three-year-old Noah Woods, it exposed a rot that goes far deeper than a single administrative error. Ten employees were abruptly removed from duty after unauthorized individuals poked around the private medical files of the toddler.
If you think this is an isolated incident, you haven't been paying attention to the systemic failures plaguing institutional data security.
The Reality of Hospital Record Snooping
Medical records are supposed to be locked down tight. Confidentiality forms the absolute bedrock of patient care. Yet, hospital gossip networks and morbid curiosity routinely override basic professional ethics.
When young Noah Woods tragically lost his life following an incident in Brantham, Suffolk, his grieving family was forced to endure an entirely avoidable secondary trauma. Ten staff members decided to look at files they had zero business opening.
Dr. Martin Mansfield, the deputy chief medical officer for the trust, called the unauthorized access completely unacceptable. He is right. But apologies after the fact do little to restore shattered confidence.
The Information Commissioner's Office is involved now, and an internal investigation is churning forward. But how did ten different people think they could access a high-profile child's confidential records without triggering immediate alarms?
Why NHS Systems Keep Failing Patients
Most people assume electronic health records feature impenetrable defense walls. They picture high-tech security dashboards flashing red the moment an unauthorized user logs in.
The reality is messy.
- Legacy computer systems often run on outdated permissions.
- Staff frequently share generic login credentials under high-pressure shift changes.
- Internal auditing tools frequently rely on post-incident reviews rather than real-time blocks.
Because of these systemic cracks, employees who have no direct care relationship with a patient can browse clinical notes unchecked until someone blows the whistle. In Noah's case, the breach piled unimaginable extra anguish onto a family already dealing with a devastating loss.
The Push for Immediate Suspension
Change is finally being forced from the top, though it took a massive media outcry to get here. NHS England chief executive Sir Jim Mackey recently issued a stern directive to trust leaders across the country.
The new mandate is simple: enough is enough.
If staff members are even suspected of snooping through patient files, they shouldn't stay on the job while a leisurely multi-week investigation takes place. They face immediate suspension and instant revocation of their system access.
This hardline approach follows separate high-profile scandals, including revelations that Southport attack survivor Leanne Lucas had her records inappropriately accessed without her knowledge for two years.
What Needs to Happen Next
Hospitals must treat unauthorized data access with the same severity as physical theft or clinical negligence. Trust is easy to lose and nearly impossible to rebuild once broken.
If you or a family member interact with the healthcare system, keep an eye on your data rights. Request audit logs if you suspect your records have been viewed improperly. Demand accountability from trust administrators.
Protecting patient privacy shouldn't require a national scandal to function properly.